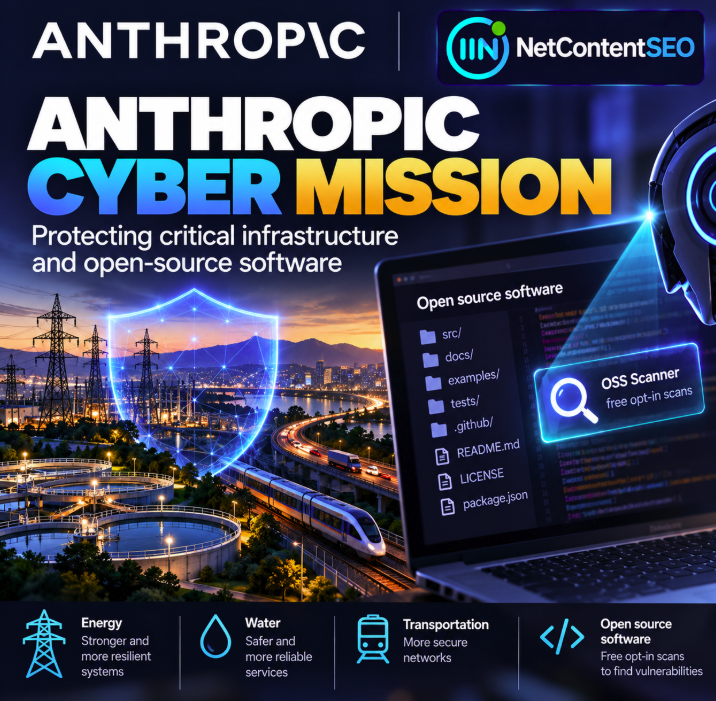
October 8, 2026 — Anthropic has launched the Anthropic Cyber Mission, a long-term initiative focused on strengthening critical infrastructure and open-source software security. Its initial efforts include the Critical Infrastructure Defense Program (CIDP), which connects advanced Claude models and Anthropic engineers with trusted infrastructure defenders, and OSS Scanner, a free opt-in AI vulnerability scanning service for open-source maintainers.
The official announcement frames the initiative as a response to increasingly capable AI-enabled cyber threats and the shortage of resources available to defenders. This is a cybersecurity program, not a search ranking update.
Two programs under the Anthropic Cyber Mission
The first, CIDP, targets operational technology (OT) used by power grids, water systems, factories and transportation networks. Anthropic says it will provide frontier Claude models, on-site engineering support and threat research through established providers. Its founding partners are Accenture, Booz Allen, CrowdStrike, Deloitte, Dragos, Hitachi, Insane Cyber, Nozomi Networks, Palo Alto Networks, PwC and Rockwell Automation.
These environments are particularly difficult to secure because systems may run continuously, use proprietary equipment and cannot always be taken offline safely to apply patches. Anthropic says the initial work is already underway with a small cohort of partners, while acknowledging that AI alone cannot solve these operational constraints.
OSS Scanner: free vulnerability reports for eligible open-source projects
OSS Scanner is an opt-in service offering periodic security scans to participating open-source projects at no charge. According to Anthropic, reports can include an explanation of a suspected vulnerability, a proof of concept and a suggested fix where available. The scans use Anthropic's most capable models.
There is an important qualification: OSS Scanner reports are generated by models and sent without human review. Anthropic expects a true-positive rate above 90%, but this is a stated expectation, not an independently verified result for the new service. Severity ratings and other details may be inaccurate. Maintainers must still triage and validate findings before changing production code.
The company says the program is best suited to projects able to process a stream of findings. For others, it will continue to use human-reviewed coordinated vulnerability disclosure procedures.
How this builds on Project Glasswing
Anthropic says Project Glasswing uncovered many software weaknesses, but finding bugs is only the beginning: verification, prioritization and safe remediation remain difficult. On October 6, the company announced an expanded Cyber Verification Program, incorporating Glasswing and widening qualified defenders' access to advanced Claude cyber capabilities. The Cyber Mission adds dedicated support, tools and funding around that effort.
What this means for technical SEO
Most SEO teams depend on software components they do not maintain themselves: content management systems, JavaScript packages, crawlers, analytics connectors, plugins, API clients and server infrastructure. Weaknesses in those dependencies can expose publishing systems, enable unauthorized content changes or disrupt site availability. An improved open-source security ecosystem could therefore help protect the technical foundations of search visibility.
However, the Anthropic announcement does not create a new Google ranking factor, change crawl-budget rules or establish a direct relationship between OSS Scanner enrollment and organic rankings. The connection to SEO is operational and indirect: safer software can help reduce outages, compromise and unwanted changes that harm a website.
Implications for AI Search and GEO monitoring
AI Search auditing tools increasingly combine browser automation, model APIs, retrieval components and scheduled data collection. These systems may inherit vulnerabilities from third-party libraries or integrations. Teams building AI visibility monitors should treat dependency security, access control and update management as part of reliable research infrastructure.
There is also a data-quality angle: if an automated system is compromised or its sources are tampered with, citation reports and AI visibility conclusions may become unreliable. This is a risk-management inference, not a specific claim made by Anthropic about search engines.
Practical security checklist for SEO and AI Search teams
- Maintain an inventory of CMS extensions, crawler libraries, SDKs and other dependencies.
- Subscribe to official security advisories for critical components.
- Apply patches in a tested environment, especially for systems with publishing access.
- Use least-privilege API credentials and rotate exposed secrets.
- Validate AI-generated vulnerability reports before treating them as confirmed.
- Monitor website uptime, unexpected content changes and indexing anomalies.
- Keep audit logs and separate research automation from production publishing permissions.
Limitations and what comes next
Anthropic plans to expand CIDP to more partners and sectors and to investigate faster vulnerability triage, patching and secure software architectures. These are future directions, not completed deployments across all infrastructure operators or open-source projects. The company also acknowledges that security fixes in operational technology may take a long time to apply safely.
NetContentSEO analysis: software supply-chain security underpins AI visibility
The most relevant takeaway for search professionals is not a new SEO tactic. It is that the reliability of SEO and GEO systems increasingly depends on the security of their software supply chains. Anthropic's Cyber Mission could help strengthen that ecosystem, provided maintainers can validate and act on the findings. For now, teams should view the program as a security development with indirect implications for search infrastructure—not as a shortcut to better rankings or AI citations.
Primary sources
Anthropic — Introducing the Anthropic Cyber Mission (October 8, 2026). Anthropic — Expanding the Cyber Verification Program (October 6, 2026).