October 8, 2026. Anthropic announced an expanded Cyber Verification Program (CVP) on October 6, introducing three verified access tiers for advanced cybersecurity work with Claude. The company is combining elements of its existing CVP and Project Glasswing initiatives to make powerful security capabilities available to more qualified defenders while applying different safeguards to different types of activity.
What Anthropic announced
The expanded program covers Claude Opus 5.5, Claude Sonnet 5.5, Claude Mythos 5.1 and future models. Unlike unrestricted general access, the new arrangement requires applicants to meet eligibility criteria and security controls based on their work. Anthropic emphasizes that cybersecurity is dual-use: techniques useful for defending systems can also be misused.
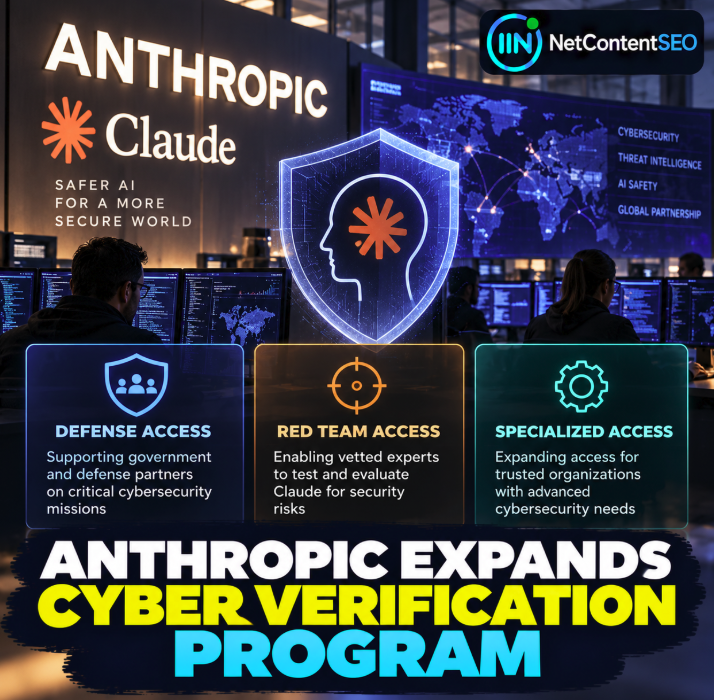
Three levels of verified access
Defense Access
Designed for defensive security operations, incident response, malware analysis and vulnerability validation. Eligible applicants can include company security teams, universities, nonprofits, government bodies, critical-infrastructure operators, open-source maintainers and individual researchers with a relevant track record. Anthropic says it aims to respond within days.
Red Team Access
Adds authorized penetration testing and red-team exercises. This tier is limited to organizations, with more demanding reviews that may take weeks. Testing must be authorized, and safeguards continue to restrict activities presenting risks of physical harm or large-scale disruption.
Specialized Access
Reserved for a small number of verified organizations working on sensitive systems, including infrastructure that could affect public safety or financial markets. Anthropic says it reviews these applicants in depth with the US government. Existing Project Glasswing members transition into this tier for their current models.
How Anthropic evaluated the safeguards
In its published CyScenarioBench testing of Claude Opus 5.5, Anthropic reports that all 50 trials were blocked at the first prompt without CVP access. Under Defense Access, 46 of 50 trials were blocked at some point; under Red Team Access, the model completed 34 of 50 tasks. These figures describe Anthropic's own evaluation under specific conditions, not independent evidence that the program eliminates misuse risks.
Project Glasswing vulnerability findings
Anthropic reports that partners identified at least 129,000 verified software vulnerabilities between April and July 2026, while its own open-source scans identified another 5,500 between April and October. More than 33,000 of the verified vulnerabilities were rated high or critical severity. The company notes that reporting is incomplete, and the figures should not be mistaken for numbers of vulnerabilities already patched.
Privacy, data retention and availability
The program generally requires data retention to monitor for cyber misuse. Anthropic says eligible organizations may later use Enterprise Frontier Safeguards, a planned solution that combines customer-controlled cloud storage with security controls. The CVP is available through the Claude Platform, Google Cloud Vertex AI and Microsoft Foundry, with Amazon Bedrock availability restricted to eligible Enterprise Frontier Safeguards customers.
What this means for SEO
This is not a Google Search ranking update. The SEO implications are indirect but important. Compromised websites can expose visitors to malicious content, inject spam pages, damage trust and disrupt crawling or indexing. Better defensive tooling may help organizations identify vulnerable code and strengthen the integrity of the websites and content systems on which search visibility depends.
What this means for AI Search
The announcement illustrates an access-control model for highly capable AI: advanced functionality can be gated by verification, authorized purpose and ongoing safeguards. It does not announce new Claude web-search citations, indexing rules, AI Overview behavior or preferential treatment for verified websites. Publishers should not confuse verification for a cybersecurity program with editorial authority or AI-search eligibility.
Practical takeaways for site owners
- Keep CMS platforms, plugins, dependencies and infrastructure patched.
- Review access controls, backups and incident-response procedures.
- Monitor unexpected URL creation, injected content and suspicious redirects.
- Use authorized security testing and record remediation work.
- Separate claims about vulnerability discovery from confirmed fixes and measurable search outcomes.
The NetContentSEO takeaway
Anthropic's expanded CVP shows how advanced AI cybersecurity capabilities may become more accessible to vetted defenders without becoming unrestricted tools. For SEO and AI Search, the relevance lies in protecting the technical and editorial integrity of websites—not in a new ranking factor.
Primary source: Anthropic, Expanding the Cyber Verification Program, October 6, 2026.