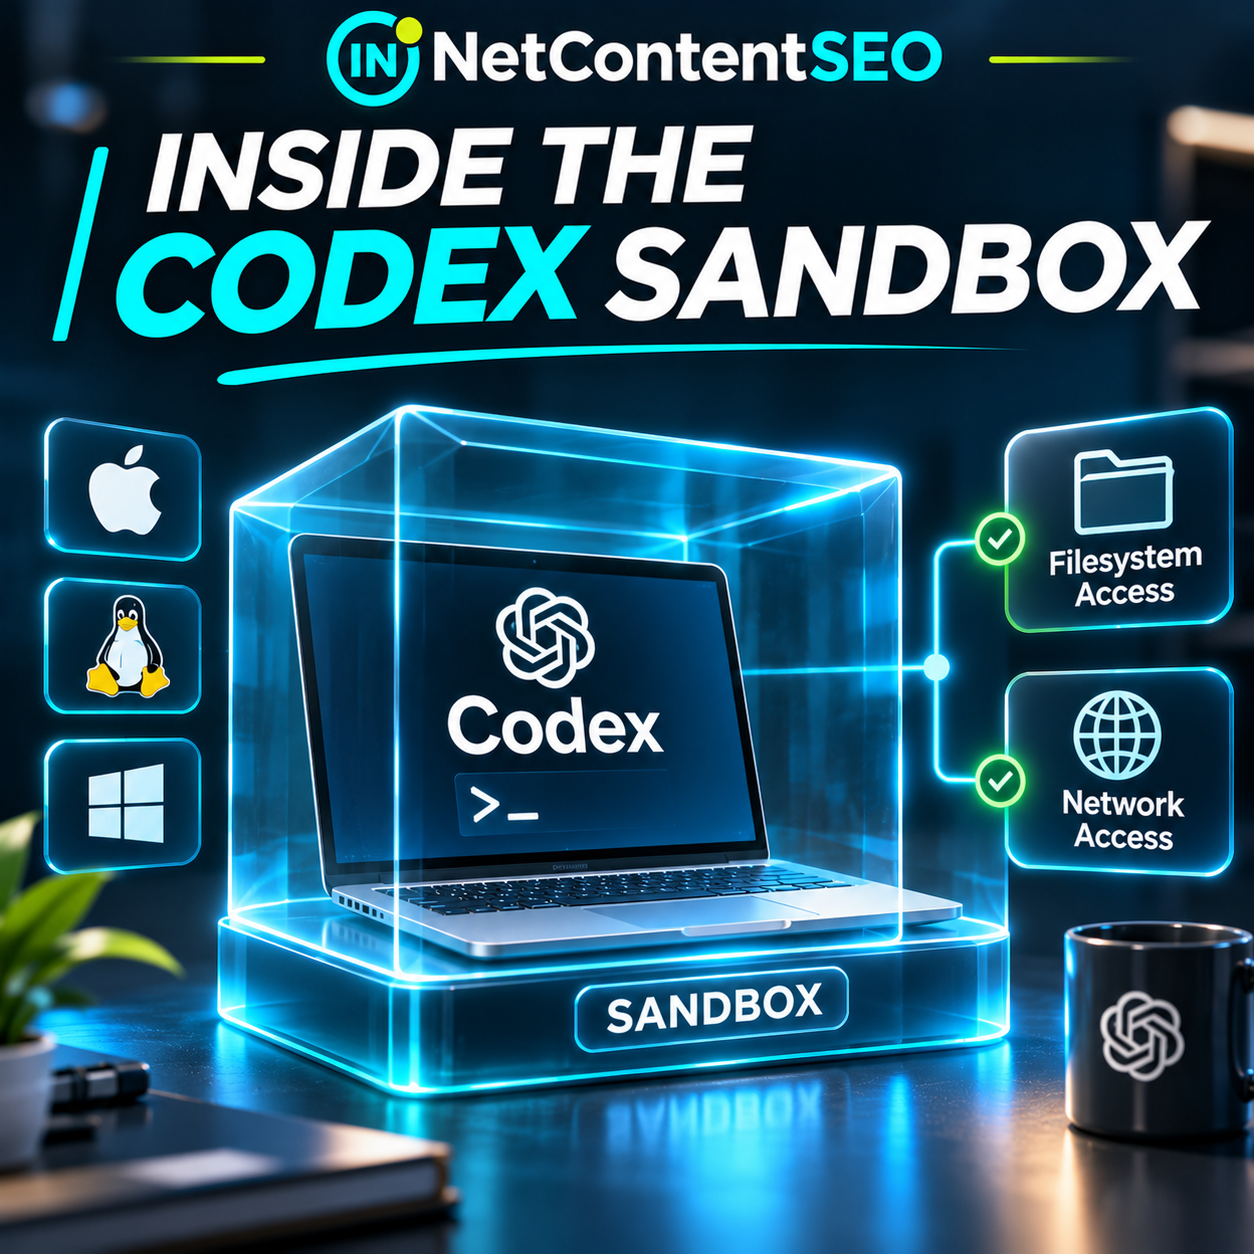
AI coding agents are becoming powerful enough to execute shell commands, modify source code, install dependencies and run tests. The critical question is no longer only what an agent can do, but what prevents it from doing something outside the developer's authorization. OpenAI's Codex sandbox addresses that question with operating-system-enforced boundaries for filesystem access and network communication, plus approval policies for operations that need broader privileges.
The supplied source, “Inside the Codex sandbox”, could not be retrieved directly during this review. This article therefore distinguishes independently verified information from OpenAI's accessible Running Codex safely at OpenAI, Windows sandbox engineering report, and sandbox documentation, rather than attributing unseen quotations or new claims to the inaccessible page.
What a sandbox actually controls
When Codex executes a command locally, the command and its child processes run under a permission profile. The sandbox defines which directories can be modified and whether network connections are allowed. An approval policy determines when the agent should stop and ask for permission to exceed those boundaries. These controls are complementary: a conversational instruction not to touch a file is weaker than a technical restriction that blocks the write.
Typical profiles include read-only work and workspace-scoped write access. The practical objective is to let an agent edit project files and run ordinary tests while protecting unrelated directories, credentials and external services. However, sandboxing is not an absolute guarantee against every vulnerability, and operations inside an allowed workspace can still be destructive if the agent makes a mistake.
How the implementation differs across operating systems
| Platform | Documented mechanism | Important distinction |
|---|---|---|
| macOS | Apple Seatbelt sandbox policies | Native operating-system enforcement for local commands |
| Linux | Linux sandboxing with bubblewrap, namespaces and kernel restrictions | Environment must support the required isolation primitives |
| Windows native | Windows-native sandbox implementations, including newer MXC and legacy elevated fallback | Capabilities and setup vary by supported version and device |
| Windows with WSL2 | Linux sandbox inside WSL2 | Linux permissions and paths apply to commands executed there |
OpenAI's documentation describes native Windows support as distinct from WSL2. The Windows engineering article explains an elevated fallback that uses dedicated sandbox accounts, restricted process tokens, filesystem ACLs and firewall rules. More recent Windows documentation also describes MXC as the preferred option on compatible devices, without the older elevated setup requirements. These are different implementations, not evidence that every Windows installation uses identical isolation.
Why blocking the network is harder than it sounds
A coding agent can invoke tools beyond its own executable: Git, Python, package managers, test frameworks and arbitrary subprocesses. Merely setting a proxy variable is not sufficient to prevent every program from opening a socket. OpenAI's Windows engineering write-up explicitly describes an earlier unelevated prototype that redirected common network tools toward a dead proxy, but found that approach too easy to bypass. The stronger legacy elevated implementation runs commands under a separate account whose outbound traffic can be blocked through firewall rules.
Managed network policies can permit approved destinations and deny others, with prompts for unfamiliar domains. That allows workflows such as downloading an approved dependency while limiting unexpected outbound connections. Network controls are particularly relevant when repositories contain untrusted instructions, malicious dependencies or credentials that should never leave the development machine.
Filesystem access and approvals: separate decisions
A workspace-write policy is intended to keep routine edits within the designated project. Additional writable roots can be configured when a workflow genuinely requires multiple directories. Approval rules govern exceptions, such as commands needing broader access. In managed environments, administrators can enforce requirements that users cannot simply override.
There is a trade-off: overly restrictive boundaries can interrupt ordinary work, while permissive settings increase the impact of errors or prompt-injection attempts. A practical approach is to grant the minimum project access required, make sensitive paths unavailable where supported, and require explicit review for operations that change production systems or access unfamiliar external services.
What OpenAI's internal deployment reveals
In its May 2026 security article, OpenAI describes managed configurations, sandbox restrictions, approval controls, network policies and agent-aware telemetry. It reports using OpenTelemetry events to understand tool executions, approvals, MCP usage and network policy decisions. These records help investigators distinguish what a process did from why the agent attempted it. Such logging is useful for operational oversight, but its availability and configuration vary by product and organization.
Five security questions every AI-agent deployment should answer
- Where can it write? Identify workspace roots, protected paths and any additional allowed directories.
- Where can it connect? Specify permitted network destinations and whether subprocess traffic is covered.
- Who approves exceptions? Make higher-risk commands explicit and reviewable.
- What secrets can it read? Keep production credentials out of routine development environments where possible.
- How can actions be audited? Preserve relevant command, approval and tool-use logs while applying appropriate privacy controls.
Why this matters for local AI, RAG and autonomous development
Local AI systems are often described as private because the model runs on a user's own hardware. That does not by itself make the entire system secure. Once a model can execute commands, read project directories or access the internet, the tool layer becomes a security boundary. A local Ollama-based agent, for example, would need its own enforced permissions and approval mechanisms; it does not automatically inherit Codex's sandbox simply because both systems run locally.
For an independent AI studio running on Windows with Ubuntu WSL2, this distinction is especially useful. The host filesystem, Linux environment, external storage and any future remote servers should be treated as separate resources with explicit access policies. A read-only research agent should not have the same capabilities as a development agent modifying code or a deployment agent touching production infrastructure.
Implications for SEO and AI Search
This is not a Google ranking update or an announcement about AI Overview visibility. Its implications for SEO are operational: agencies and publishers increasingly use agents to inspect websites, analyze Search Console exports, process logs, update templates and automate technical audits. A sandbox can reduce the risk that a routine analysis modifies unrelated files, exposes credentials or sends internal data to an unintended destination.
For AI Search products, the same principle applies to retrieval and browsing tools. Untrusted webpages and documents can contain prompt-injection instructions. Source text should be treated as evidence to analyze, not as permission to execute commands or change security settings. Strong isolation, restricted tools, source validation and human review all contribute to a safer workflow.
Limitations and unanswered questions
Security controls depend on the operating system, product surface, configuration and version. The accessible documentation establishes the overall architecture and several platform-specific mechanisms, but does not prove that every Codex deployment has identical defaults or that all attacks are prevented. The exact contents and publication details of the supplied “Inside the Codex sandbox” page could not be confirmed directly, so any unique examples from that page remain unverified.
FAQ
Does Codex run commands directly on my computer?
In local workflows, yes: commands execute on the user's machine, subject to the configured sandbox and approvals. Cloud-hosted Codex environments are separate from the user's local host.
Does a sandbox mean Codex cannot delete files?
No. It can still modify or delete files within directories where it has write permission. Sandboxing limits the scope of access; it does not guarantee that every authorized action is correct.
Is network access always disabled?
Network access depends on the configured policy and execution environment. Some modes restrict it by default and require permission for broader access.
Does Windows require WSL2?
No. Codex supports native Windows sandboxing as well as Linux sandboxing through WSL2, with different technical implementations.
Does this make AI-generated code secure?
No. Sandboxing constrains execution privileges; generated code still requires tests, code review, dependency scrutiny and appropriate deployment controls.
Does the sandbox improve SEO rankings?
No direct ranking benefit has been announced. The value for SEO teams lies in safer automation of technical workflows.
Conclusion: autonomy needs enforceable boundaries
Codex illustrates an important shift in AI software development: the safest agent is not necessarily the one that promises to behave, but the one whose permissions are technically bounded and whose exceptions are visible. Operating-system sandboxing, scoped filesystem access, network policies and approval workflows make it more practical to delegate real development work without giving an AI agent unrestricted control. The broader lesson extends well beyond coding—to local AI studios, SEO automation, RAG pipelines and every system where language models can act on the world.
Sources: Supplied OpenAI article (direct retrieval unsuccessful); OpenAI, Running Codex safely at OpenAI; OpenAI, Building a safe, effective sandbox to enable Codex on Windows; Official sandbox documentation; Official Windows sandbox documentation. Barry Schwartz: NOT CHECKED.